Attackers exploit fake STM32 vulnerability alert to target Trezor and BitBox holders
Trezor confirms an email-provider breach and says its wallets remain safe, while BitBox investigates a likely newsletter-provider compromise.

Trezor confirms an email-provider breach and says its wallets remain safe, while BitBox investigates a likely newsletter-provider compromise.

An authorization flaw in Brevo’s login system has allowed an attacker to access 138 customer accounts, leading to phishing emails sent through accounts used by Trezor, BitBox and CoinTracking. Brevo said in a Thursday postmortem that the attacker exploited a…

Trezor told Cointelegraph that the phishing email was sent to 347,000 subscribers and said it is treating every address as “known to the attacker and possibly reusable for phishing.”

Bitcoin Magazine Trezor Reveals Another Data Breach After Scammers Target Marketing Platform Users of the bitcoin hardware wallet were targeted with phishing attacks. This post Trezor Reveals Another Data Breach After Scammers Target Marketing Platform first appeared on Bitcoin Magazine and is written by Mathew Di Salvo .

Trezor revealed that hackers were able to access its email domain, which it's since taken down, and is now launching an investigation.

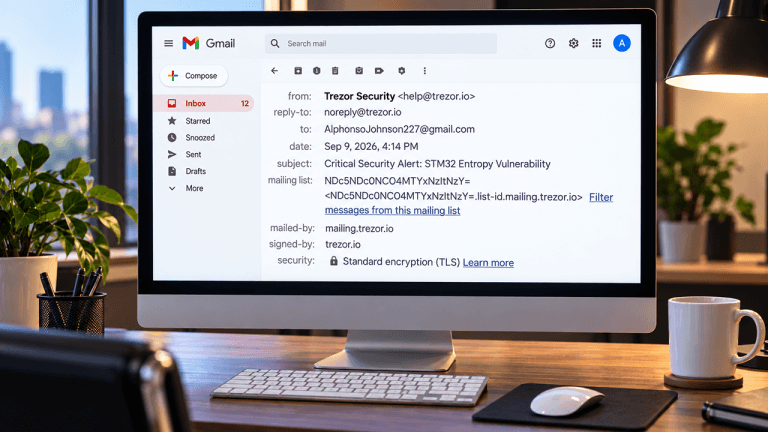
Trezor has confirmed that a third-party email service provider it uses was breached, allowing attackers to send phishing emails directly from the firm’s own legitimate domain. The fraudulent email carried the subject line “Critical Security Alert: STM32 Entropy Vulnerability,” designed to convince recipients that their hardware wallets were compromised and

Trezor, Bitbox, and Cointracking warned customers Thursday that phishing emails were sent through compromised mailing infrastructure, turning what looked like legitimate security notices into traps designed to steal information from cryptocurrency users. The incident that occurred on Sept. 9 and 10 appears to stretch beyond a single company. Bitbox said multiple bitcoin companies were targeted […]

Hardware wallet makers Trezor and BitBox have warned users about phishing emails disguised as urgent security notices after suspected compromises involving third party email services. Trezor said on Wednesday that its email provider had been breached and warned users not…

Trezor users are being targeted again with sophisticated phishing messages.

Trezor users have been hit by an unusually sophisticated phishing campaign after attackers breached a third-party email provider.

BitBox said multiple Bitcoin companies appeared to have been targeted through a shared newsletter provider, while Trezor confirmed a breach at its email service.

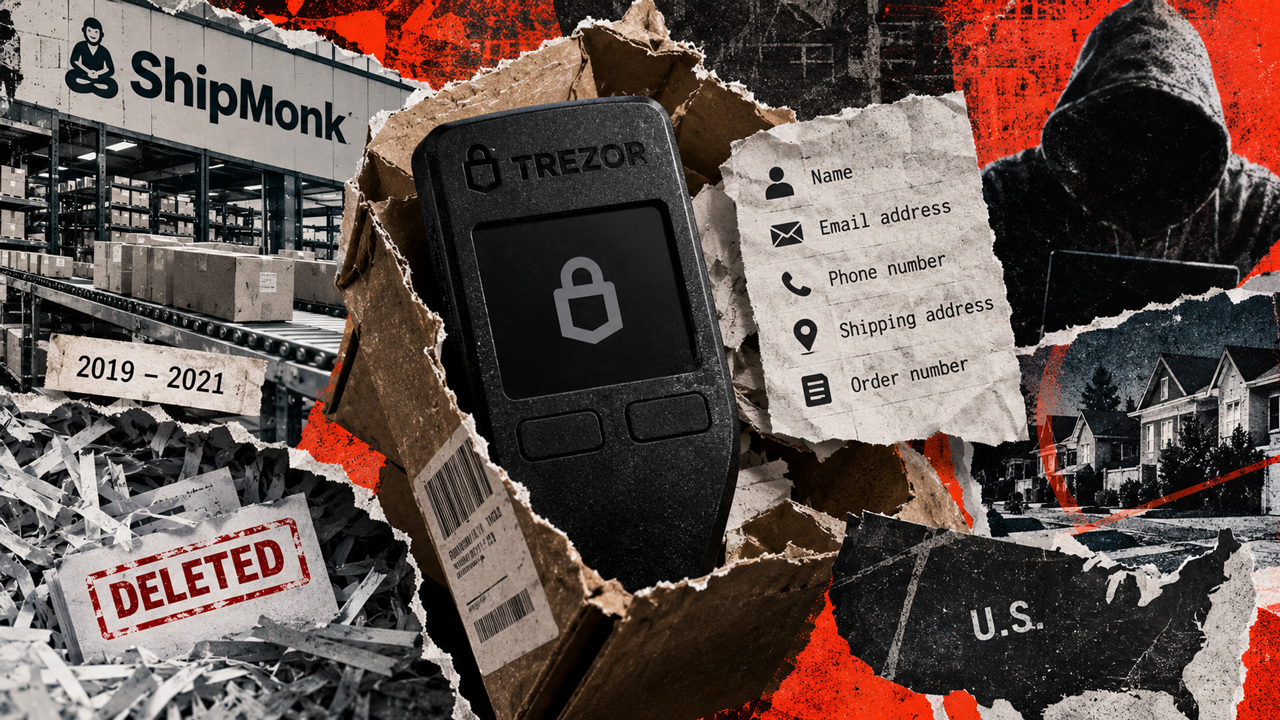
This follows last month's security breach at shipping provider ShipMonk, which exposed the personal information of Trezor customers.

The hardware wallet maker said a fake security alert claimed a hardware flaw could expose users’ recovery phrases.

Trezor has warned customers not to click links in a fraudulent security email sent after a third-party provider was breached.
Trezor confirmed a third-party email provider breach that pushed fake STM32 security alerts to wallet users.

Clear signing enhances transaction transparency, reducing risks in crypto security and pushing DeFi protocols towards greater accountability.

Ledger and Trezor said researchers have a responsibility to publish their findings if vendors fail to fix bugs within an agreed disclosure window.

The collaboration between Ledger and Trezor highlights the urgent need for industry-wide security standards as AI accelerates vulnerability exploitation.

Trezor disclosed that a data breach at former shipping partner ShipMonk exposed full personal and order details of approximately 67,000 additional US customers from 2019-2021 orders. The expansion stems from records that were supposed to have been deleted despite repeated written assurances.

The larger disclosure implies roughly 80,689 affected customers, though no combined total or row-level overlap check is public.